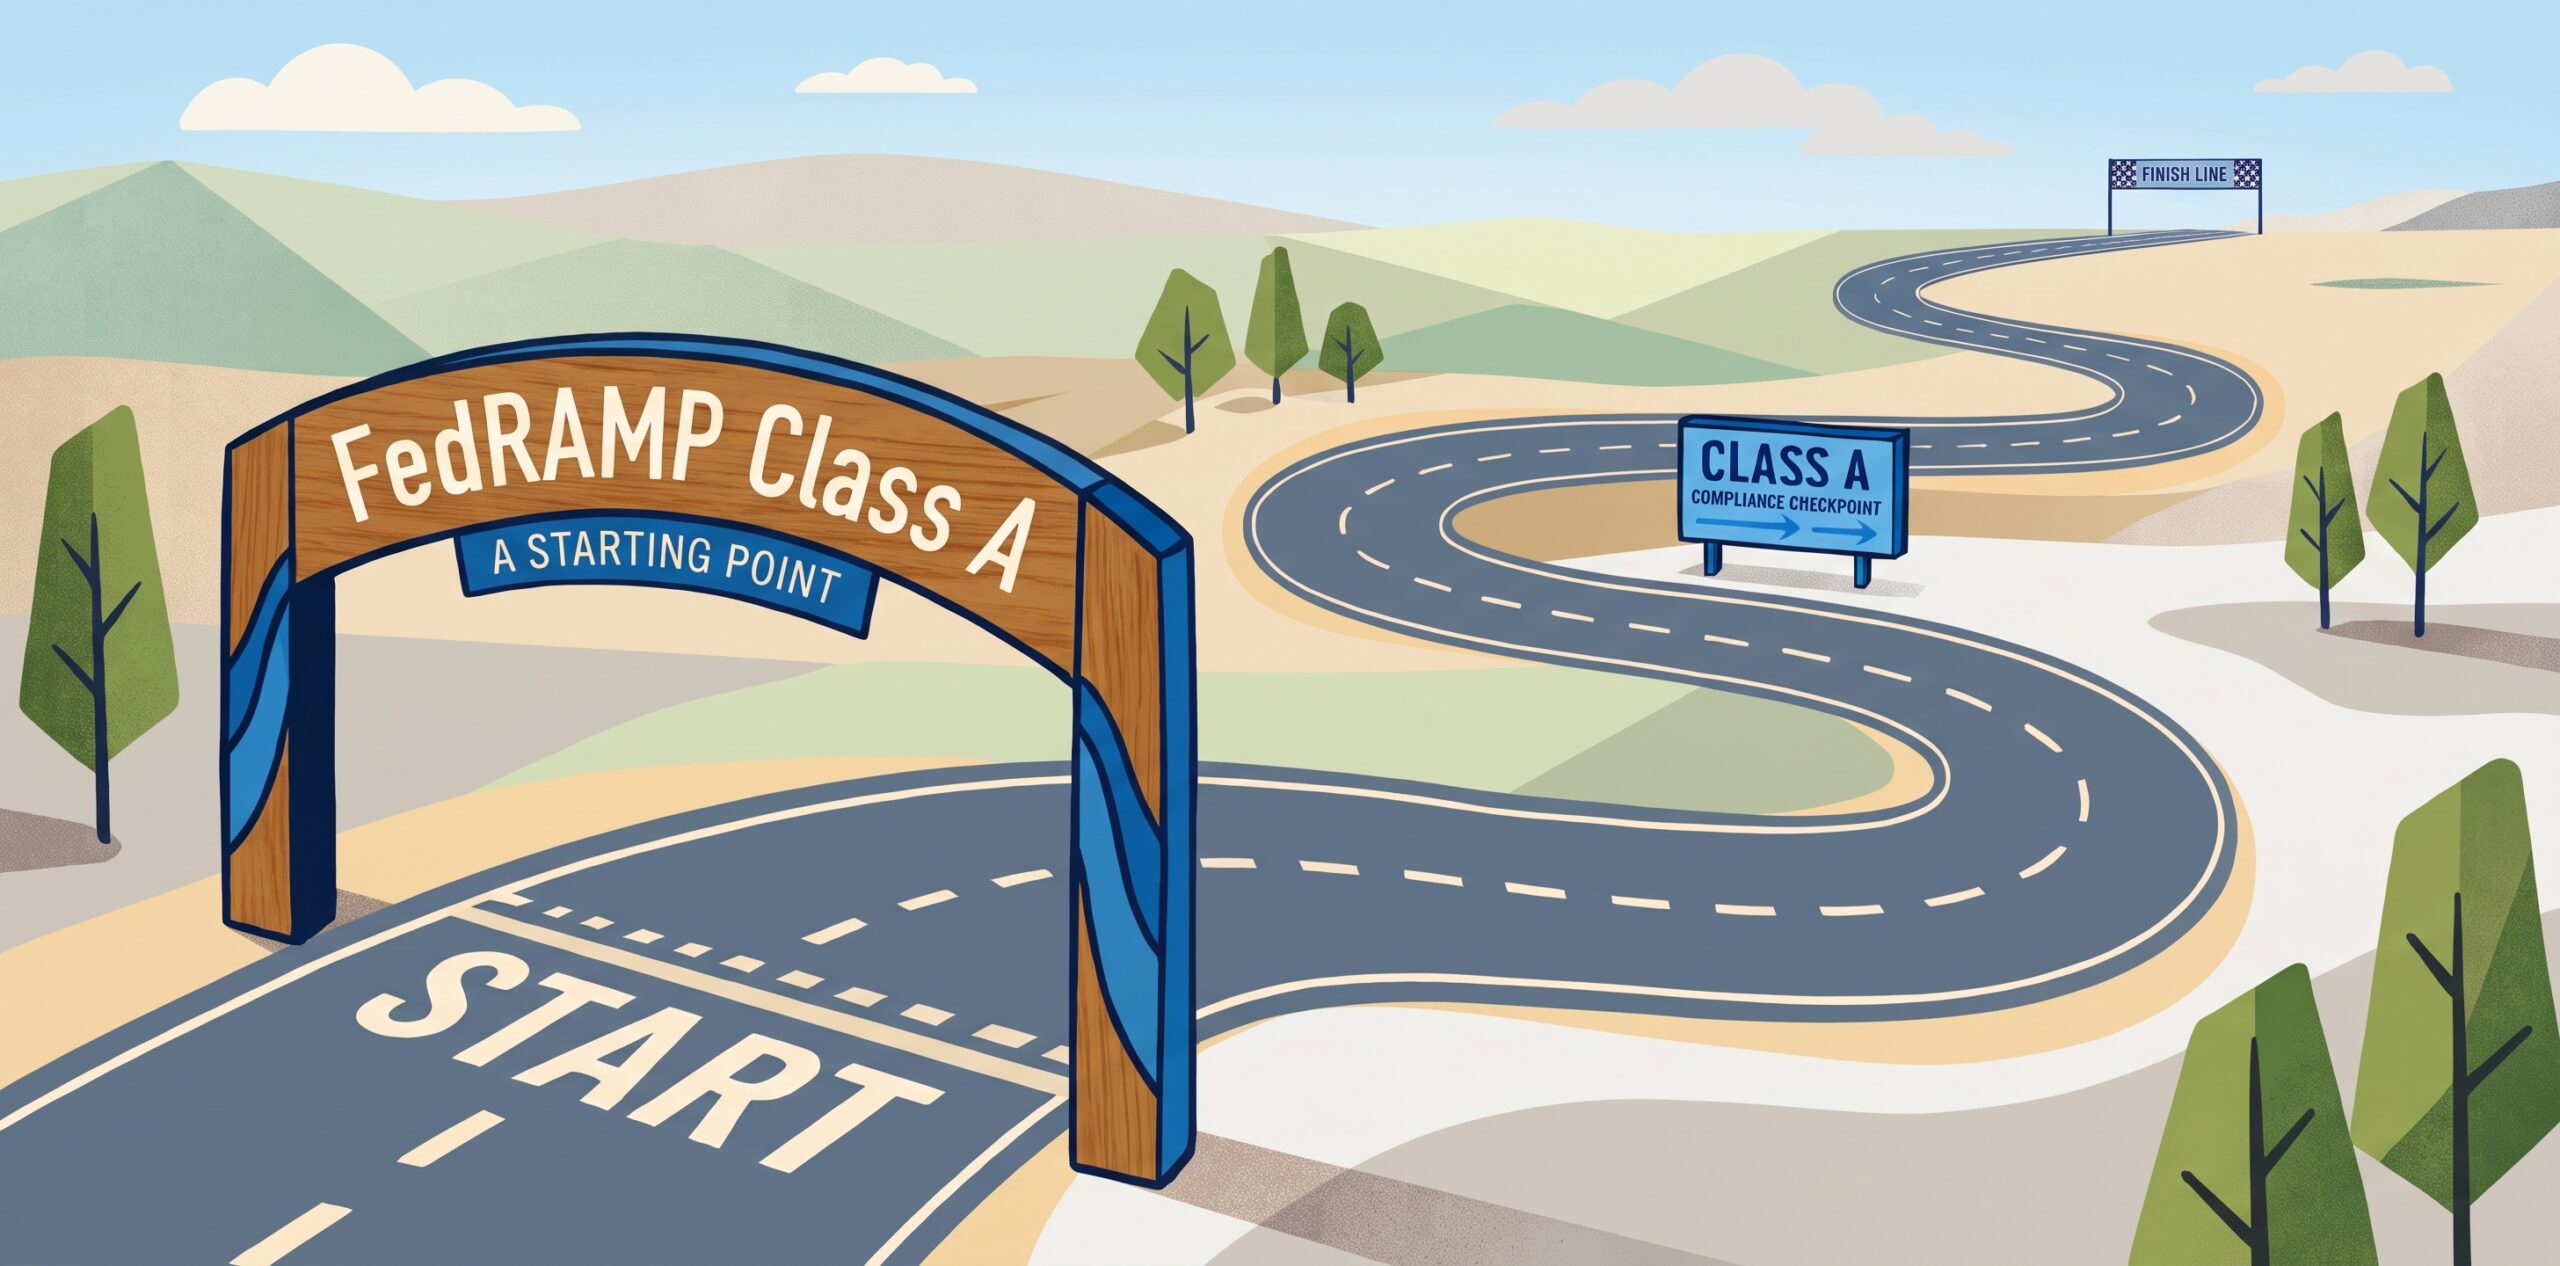
The FedRAMP Consolidated Rules for 2026 (CR26) introduced Certification Classes A through D, replacing the familiar Low, Moderate, and High designations. One of the more significant changes (though temporary) is Class A, which provides a new entry point for cloud service providers (CSPs) looking to enter the federal market.
For SaaS providers with existing commercial security assessments, Class A offers an opportunity to gain FedRAMP Marketplace visibility without first completing a traditional FedRAMP assessment. But there is an important distinction between being listed in the Marketplace and meeting the security requirements for a specific federal agency. Understanding that distinction is critical when determining where Class A fits into a CSP’s broader FedRAMP strategy.
What Class A Actually Provides
Class A creates a path for CSPs to leverage existing security assessments rather than starting the FedRAMP process from scratch. Under CR26, eligible CSPs can use an assessment completed within the previous 12 months under an approved framework, including SOC 2 Type II, GovRAMP, or qualifying FedRAMP Rev. 5 assessments. This allows CSPs to build on security work they have already completed, without requiring an initial agency sponsor or the same independent FedRAMP assessment required for Classes B, C, and D.
For organizations that have already invested in commercial security compliance, this is a meaningful change. However, Class A is not equivalent to a traditional Moderate or High authorization. It does not establish that a cloud service offering meets every requirement for a particular federal workload, nor does it replace an agency’s responsibility to evaluate risk before deploying the service.
Class A provides a path into the federal market. It does not automatically qualify a CSP for every federal opportunity, not does it offer a permanent certification status.
Understanding When Class C or D Is Needed
For many CSPs, Class A will be a starting point rather than the final certification goal. Federal agencies must evaluate cloud services based on the sensitivity of the information being processed and the impact of a potential security compromise. For systems processing Controlled Unclassified Information (CUI), sensitive financial information, or supporting higher-impact missions, agencies may require Class C or Class D certification.
These classes involve more extensive security requirements, independent assessments, and ongoing validation. Department of Defense (DoD) workloads may also require additional security requirements under the DoD Cloud Computing Security Requirements Guide (CC SRG), including applicable Impact Level 4 or 5 requirements.
Class A does not eliminate those obligations.
This is why CSPs should consider their target federal customers and intended workloads before selecting a certification path. If your customers require Class C, achieving Class A may provide earlier visibility, but it does not remove the work required to meet Class C requirements.
Building on Existing Assessments
One of the more practical benefits of Class A is the ability to reuse existing assessment work. OMB Memorandum M-24-15 emphasized reducing duplicative security assessments and making better use of existing security information.
Class A puts that direction into practice by recognizing approved alternative security frameworks.
For CSPs with a recent SOC 2 Type II, GovRAMP, or qualifying FedRAMP Rev 5 assessment, this creates an opportunity to establish a FedRAMP presence while preparing for additional certification requirements. Existing assessment evidence may also support future FedRAMP work, particularly in areas such as access control, logging, encryption, and security monitoring. However, evidence reuse does not mean requirements are automatically satisfied.
CSPs still need to demonstrate that their implementations meet the applicable FedRAMP requirements, and independent assessors must validate that the evidence supports those claims. This becomes particularly important under FedRAMP 20x, where Key Security Indicators (KSIs), automated validation, and continuously maintained security evidence play a larger role.
The opportunity is to reuse existing security work where it makes sense, not to assume one assessment satisfies another framework.
Making Class A Part of a Longer-Term Strategy
The right certification path depends on the CSP’s federal market objectives. For some organizations, Class A may provide an appropriate level of assurance for their intended customers and use cases. For others, particularly those targeting agencies with Moderate- or High-impact workloads, Class A may be an intermediate step toward Class C or D.
CSPs considering Class A should be asking a few practical questions:
- What certification class will our target federal customers require?
- Can we leverage an existing SOC 2 Type II, GovRAMP, or qualifying FedRAMP assessment?
- Which existing security implementations and evidence can support our future certification requirements?
- What additional KSIs, automated validations, and continuous monitoring capabilities will we need?
- Does pursuing Class A first support our business objectives, or would it make more sense to proceed directly toward Class B, C, or D?
- Are we prepared to achieve Class B, C, or D before our temporary Class A status expires?
These decisions should be made early, particularly when CSPs are designing their FedRAMP compliance processes and investing in automation. For organizations planning to pursue Class C or D, the goal should be to build security and compliance capabilities that can support those requirements from the beginning. That includes identifying reusable evidence, integrating automated validation into existing processes, and maintaining accurate Security Decision Records (SDRs).
The Bottom Line
Class A is a meaningful addition to FedRAMP. It recognizes existing commercial security assessments and provides another path for CSPs to enter the federal market. But Marketplace visibility and agency procurement readiness are not the same thing. CSPs need to understand the requirements of their target customers and choose a certification strategy that supports those requirements.
If eligible, use Class A to gain Marketplace visibility while building toward Class B or Class C under 20x, where those higher classes are needed.
The real opportunity is not simply getting listed in the Marketplace sooner. It is leveraging existing security investments while building a sustainable approach to continuous compliance.